CSP#
On this page can set the Content Security Policy (CSP) and various other security HTTP headers.
External link
https://developer.mozilla.org/en-US/docs/Web/HTTP/CSP
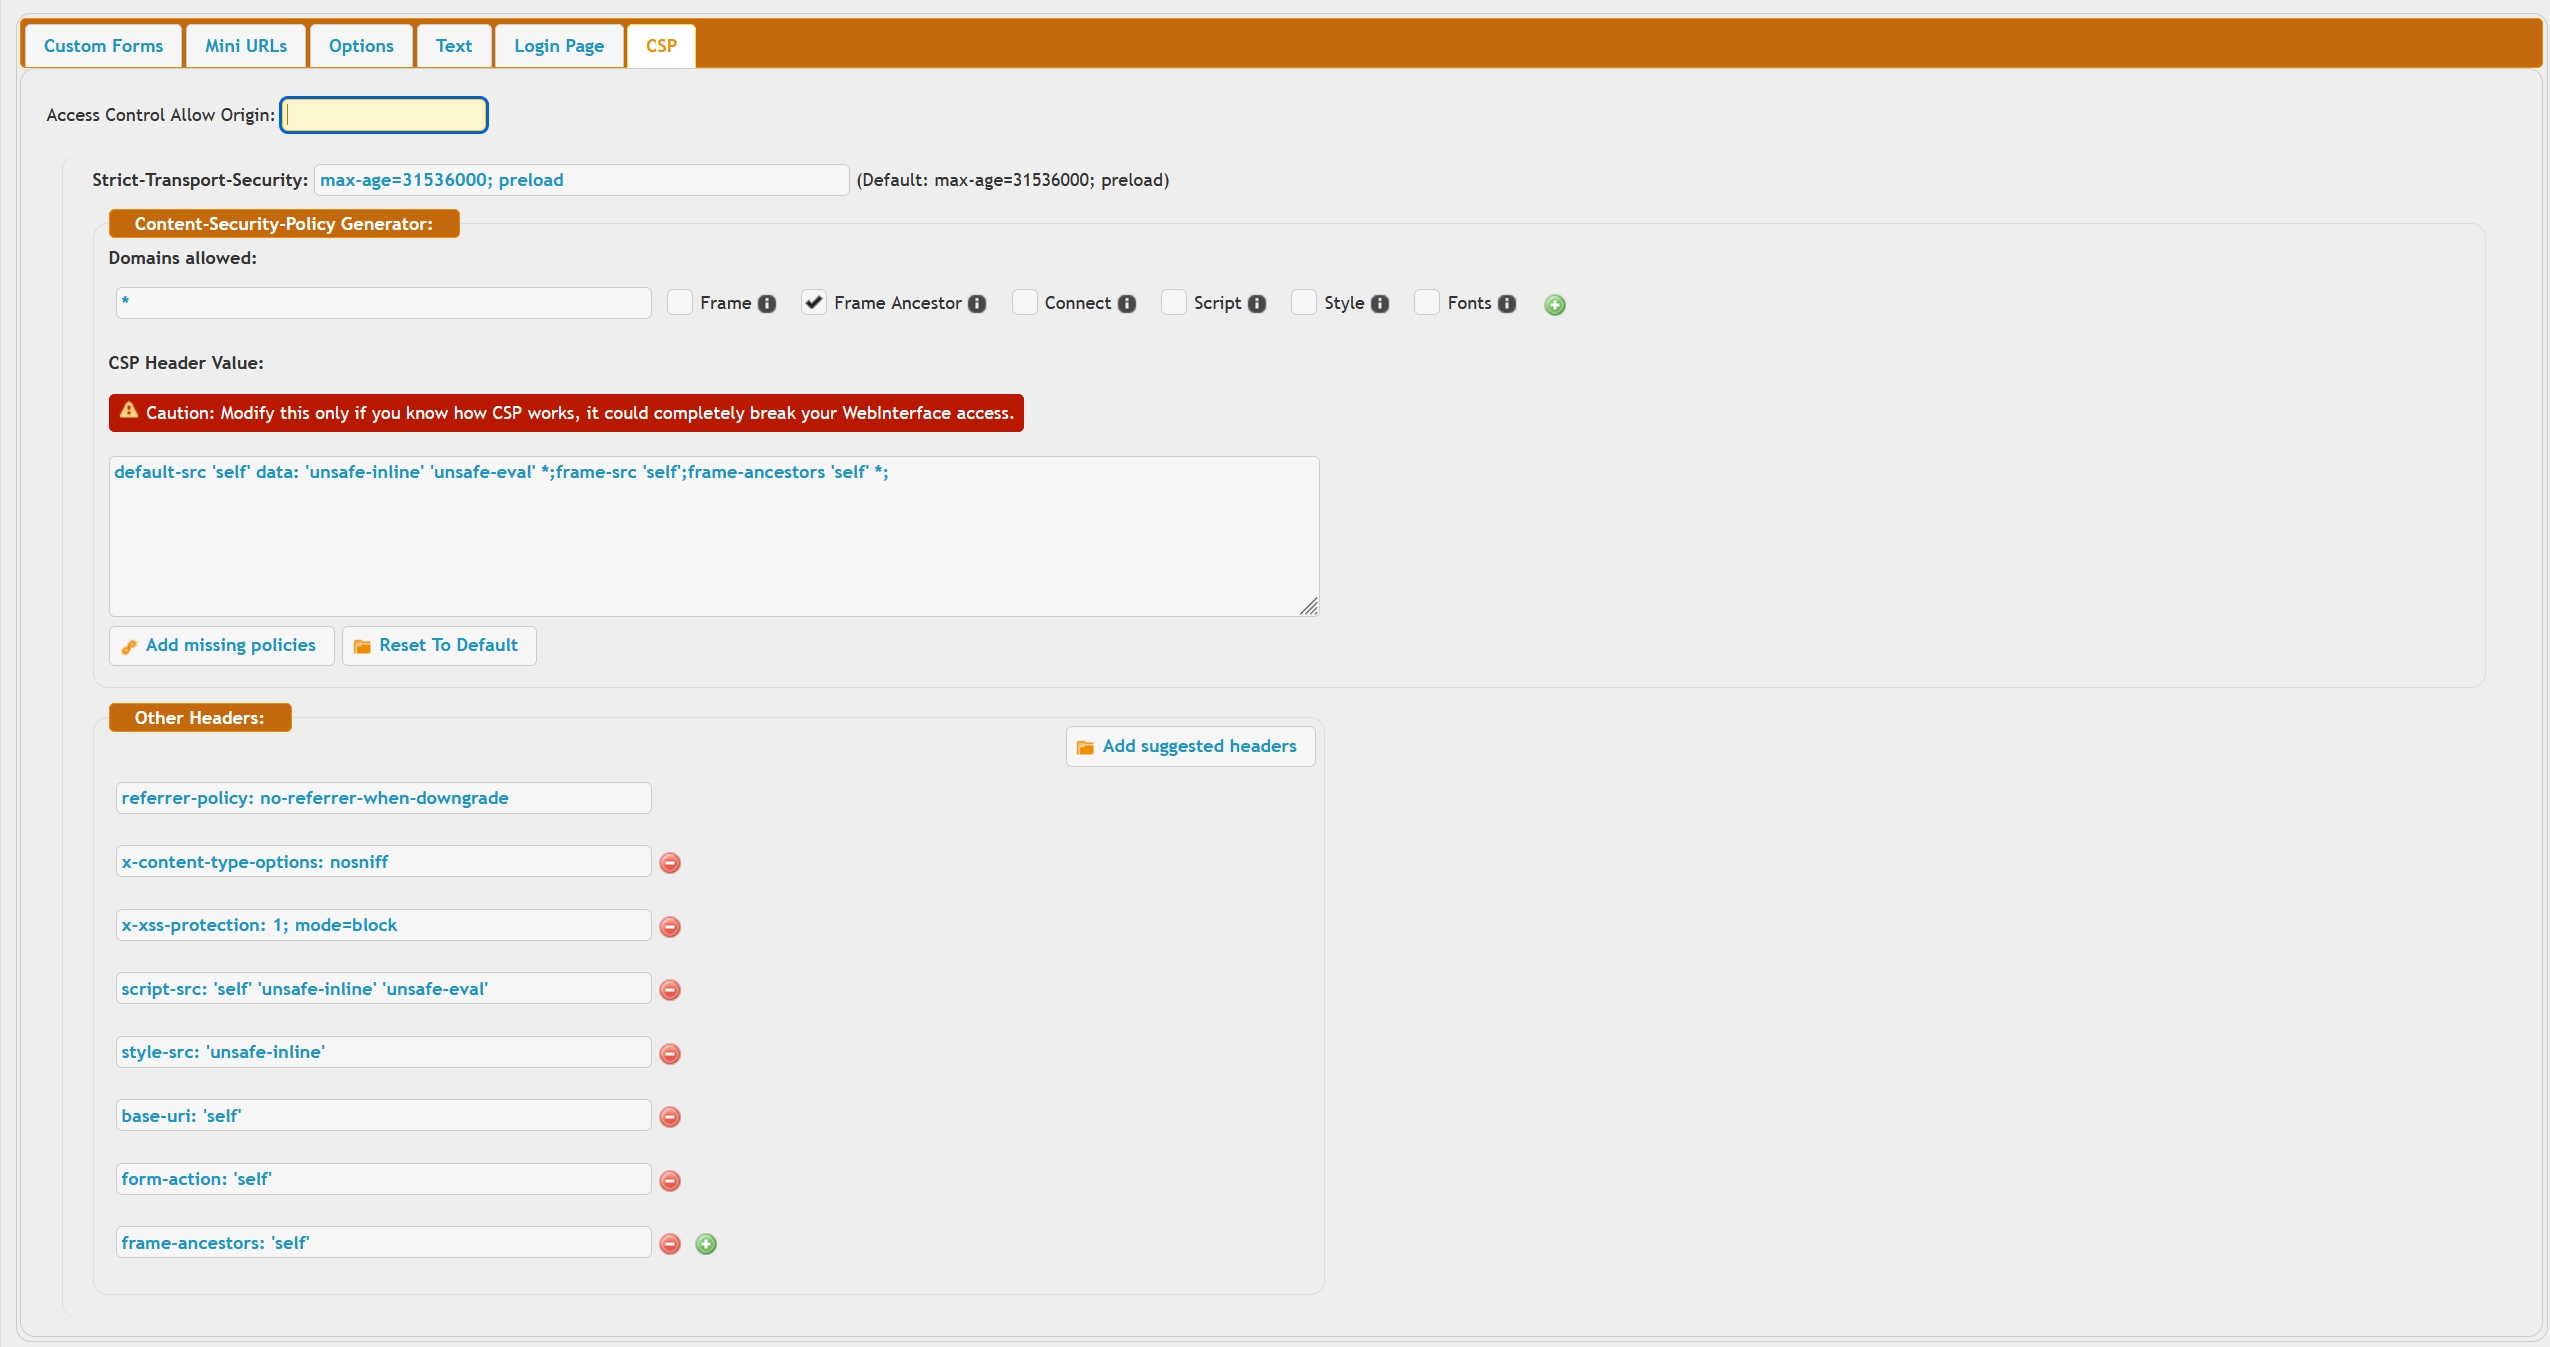
The CSP header comes with default policy
Content-Security-Policy: default-src 'self' data: 'unsafe-inline' 'unsafe-eval'
editable in the GUI. The Domains Allowed field values extend the policy with external source domain directives.
The Other Headers section allows adding miscellaneous headers, the format required is
Header-Name:header value #1;header value #2;
We set the following security headers by default:
- HSTS External link: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Strict-Transport-Security
- Referrer-Policy External link: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Referrer-Policy
- X-Content-Type External link: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/X-Content-Type-Options
- XSS policy headers External link: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/X-XSS-Protection
- Cache Control policy headers External link: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Cache-Control
Can add up to 20 additional headers in this section. This may be extended in future releases.