Google Cloud Storage Integration#
1. Google Cloud Storage REST API#
Cloud Storage JSON REST API based integration: Cloud Storage JSON REST API Link
⚠️ Proxy Configuration: If your server accesses the internet through a proxy, make sure to whitelist the following domains for Google Authentication and Storage access:
- oauth2.googleapis.com
- storage.googleapis.com
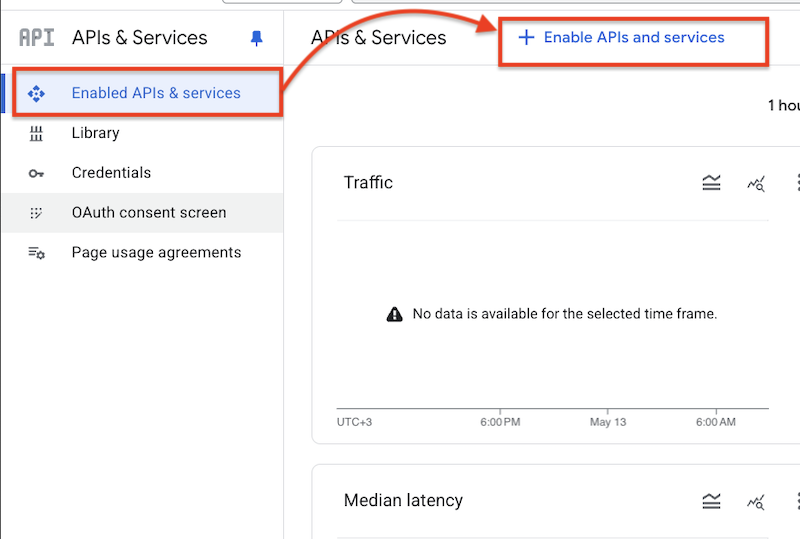
Start by navigating to Google APIs & Services: Google APIs & Services Link
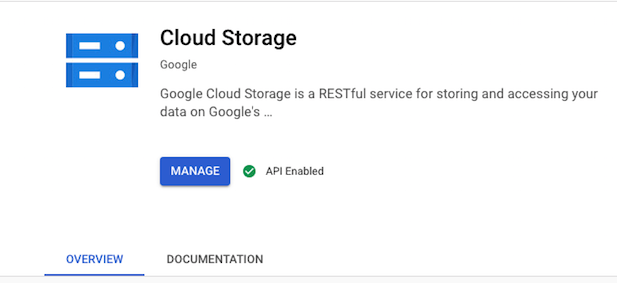
⚠️ Important: Ensure the Cloud Storage is enabled at Enabled APIs & services. Google API Library Link
1.1 Configure access through a Web Application OAuth client#
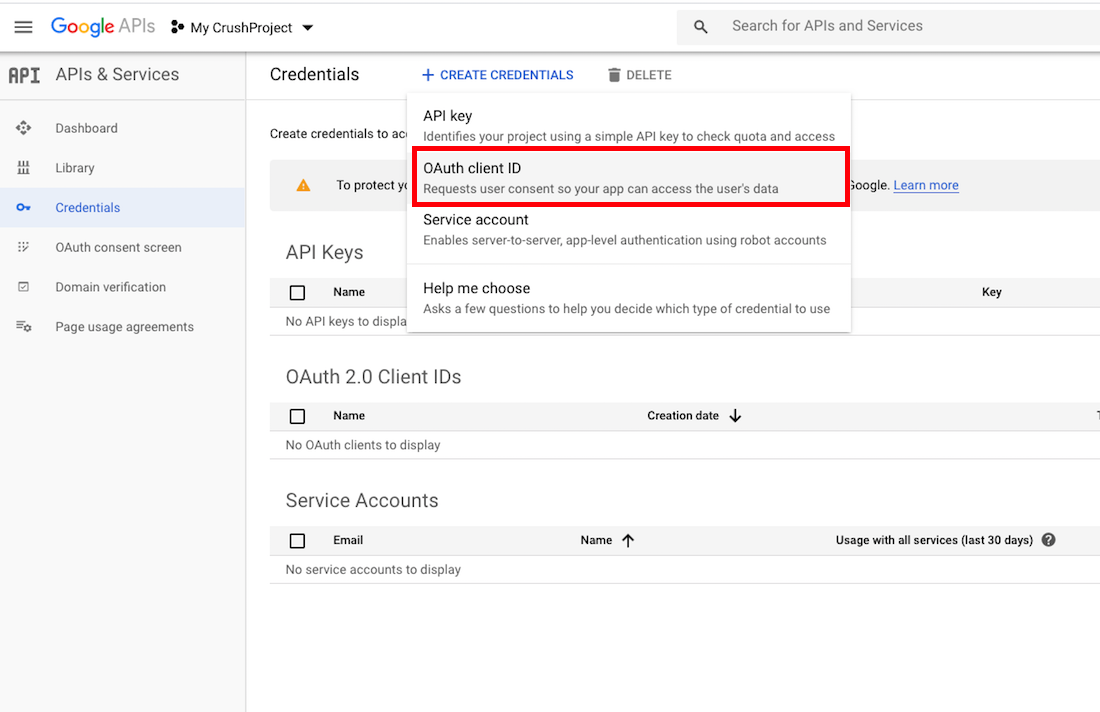
Go to the Credentials menu, click on Create Credentials, and select OAuth client ID:
• Select the application type: Web application.
• Provide a unique name to identify your OAuth client (e.g., CrushFTP Integration).
Then configure the following:
• Authorized JavaScript origins: Add the base URL of your CrushFTP server (e.g., https://your-domain.com).
• Authorized redirect URIs: This is the URL Google will redirect to after successful authorization. The Redirect URL must end with ?command=register_gdrive_api
    http://127.0.0.1:9090/?command=register_gdrive_api
    or
    https://your.crushftp.domain.com/?command=register_gdrive_api
Finally, click the Create button.
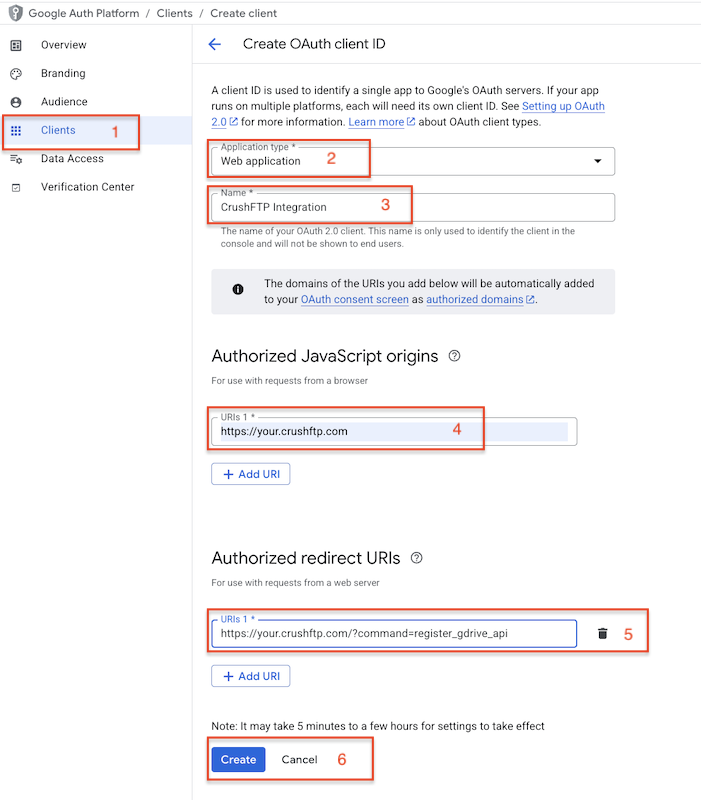
After the credentials are created, copy the Client ID and Client Secret.
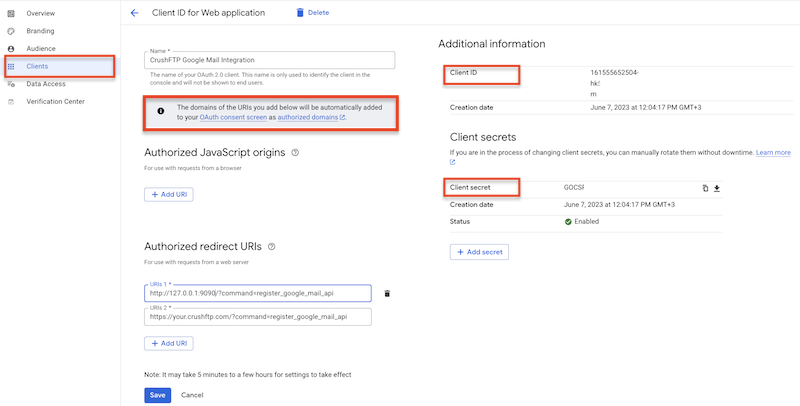
⚠️ Note: You can configure the OAuth consent screen by clicking the link above the Authorized JavaScript origins section:
"The domains you enter in the fields below will be automatically added to your OAuth consent screen as authorized domains."
Click the link to open the OAuth consent screen settings, complete the configuration, and authorize your CrushFTP domain.
Important: After configuration, don’t forget to click Publish App at Audience page to make it active. Without publishing, the app will remain in Testing mode, which restricts access to authorized test users only.
GStorage Remote Item Settings:
Select the GStorage item type and click the Get Refresh Token button.
⚠️ Important: To obtain the Refresh Token, the CrushFTP WebInterface’s host and port must match the Redirect URL specified in the Google APIs & Services-> Credentials -> OAuth 2.0 Client IDs. In our example, it was: http://127.0.0.1:9090 or https://your.crushftp.domain.com/
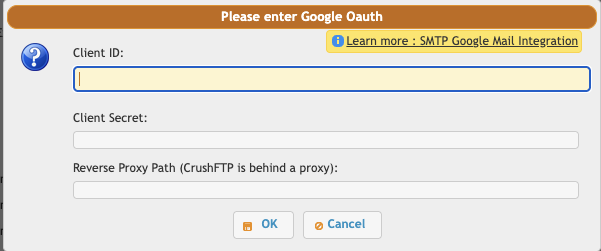
Enter the Client ID , Client Secret. Proceed with the authentication and authorization process.
⚠️ Important: Be sure to sign in with the Google Account that has the necessary permissions, as configured in the Google APIs & Services-> Credentials -> OAuth 2.0 Client IDs. This will automatically configure the User name and Password.
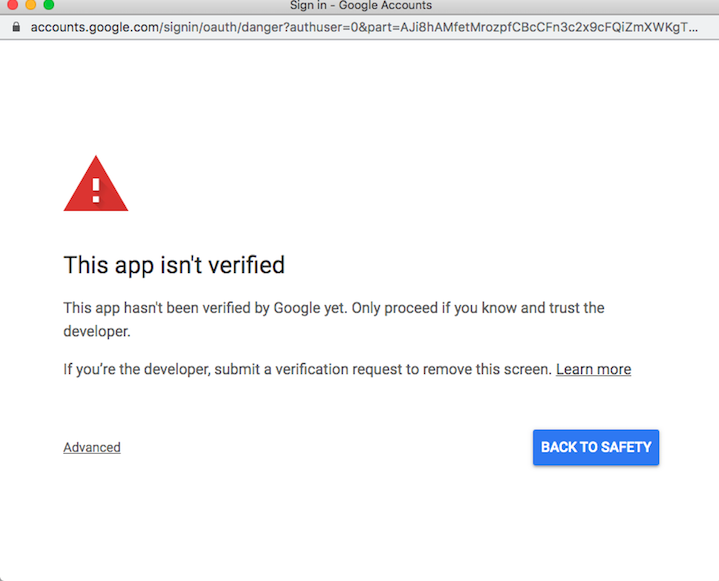
If the domain is unverified, a warning message may appear. Click Advanced and choose to proceed:
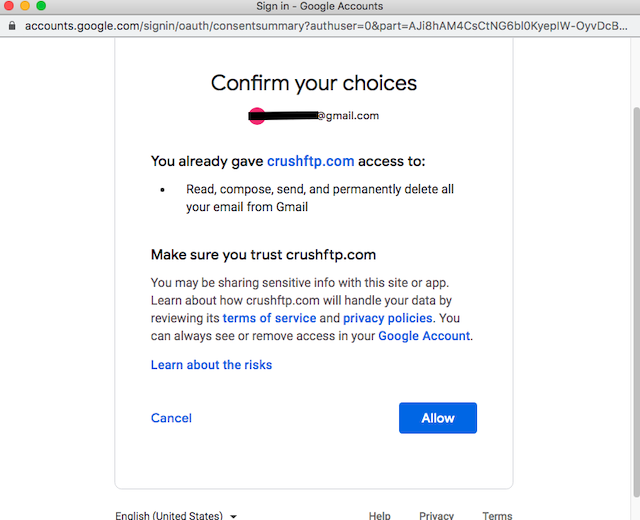
Click on the Allow button:
Provide the Google Storage Bucket and the path.
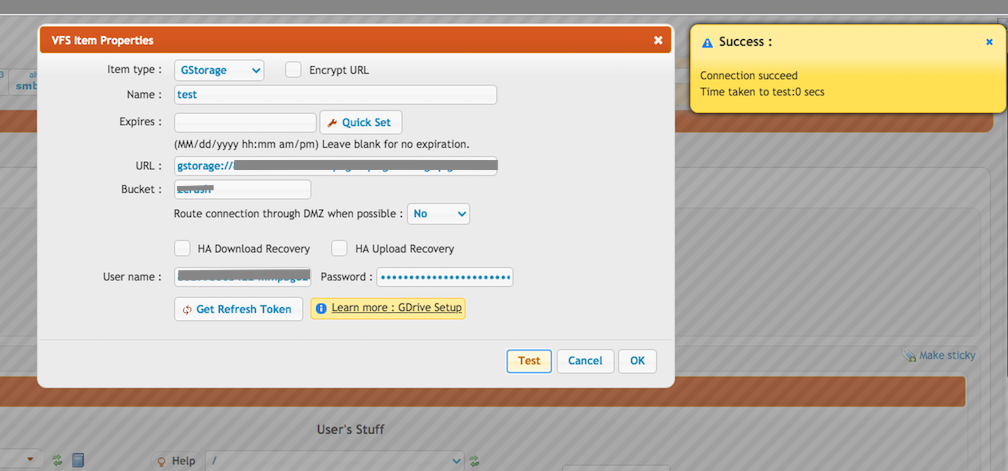
1.2. Configure access using a Service Account OAuth client#
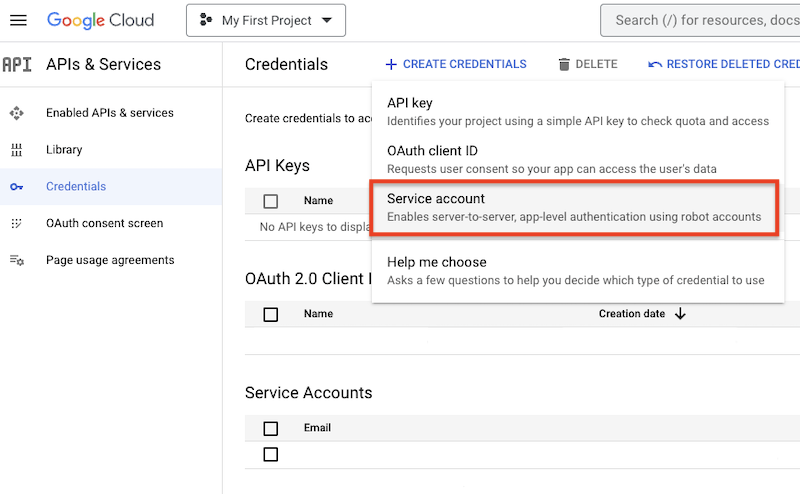
Create Credentials -> Service Account.
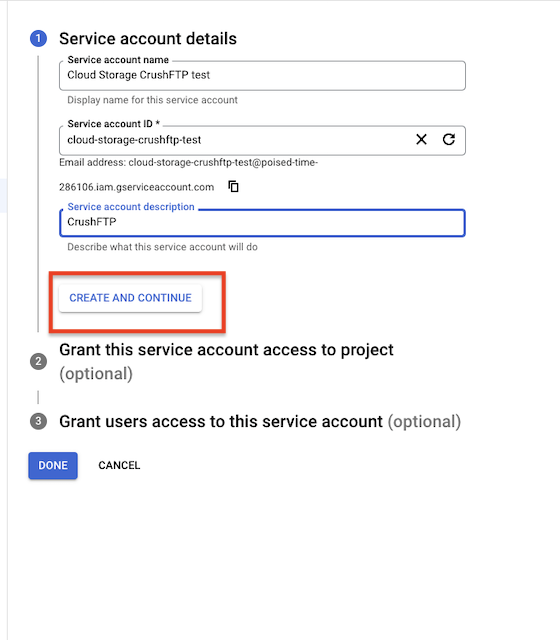
Provide a name and continue.
Configure the service account access.
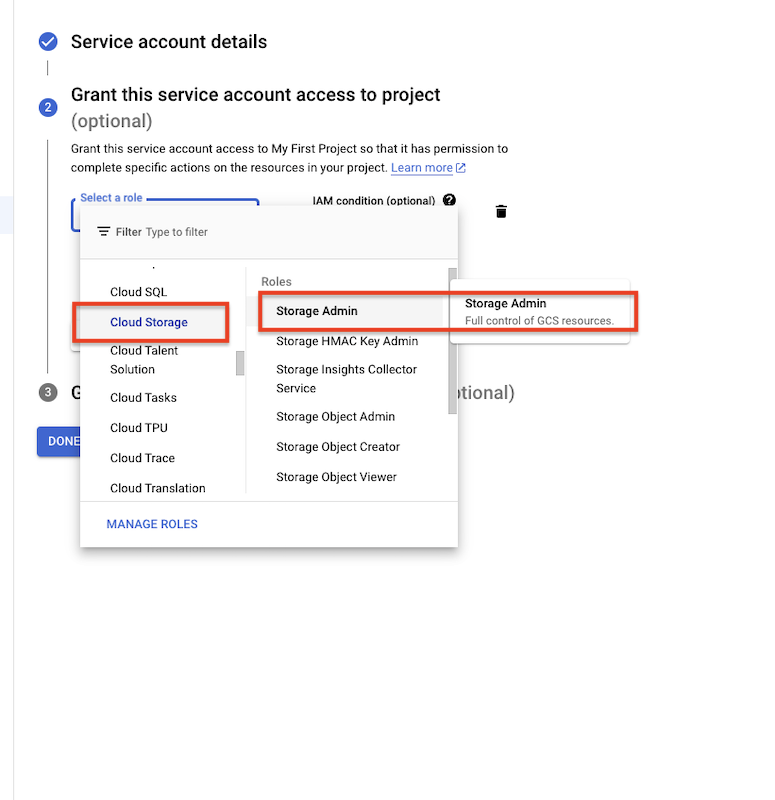
Click on the Done button.
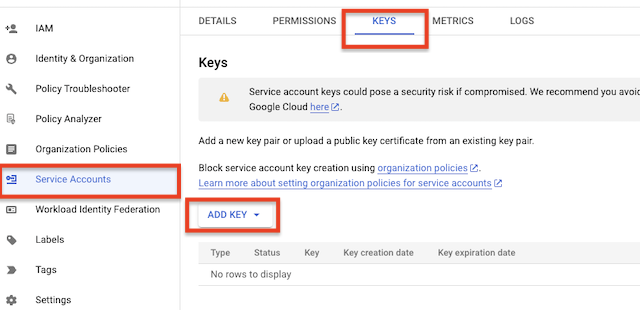
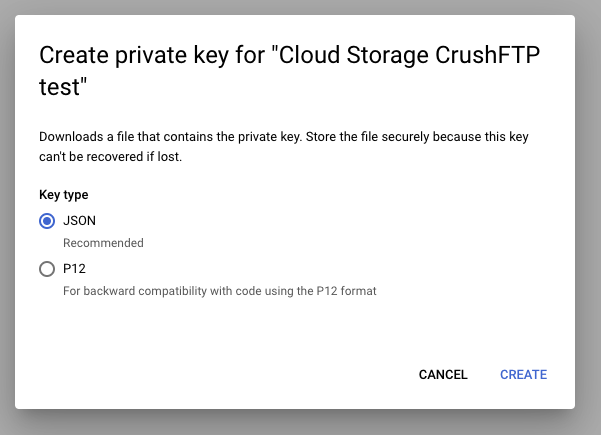
Navigate to the newly created Service Account. Go to the KEYS tab. Click on the Add KEY button, and then select Create new key.
Download the JSON file.
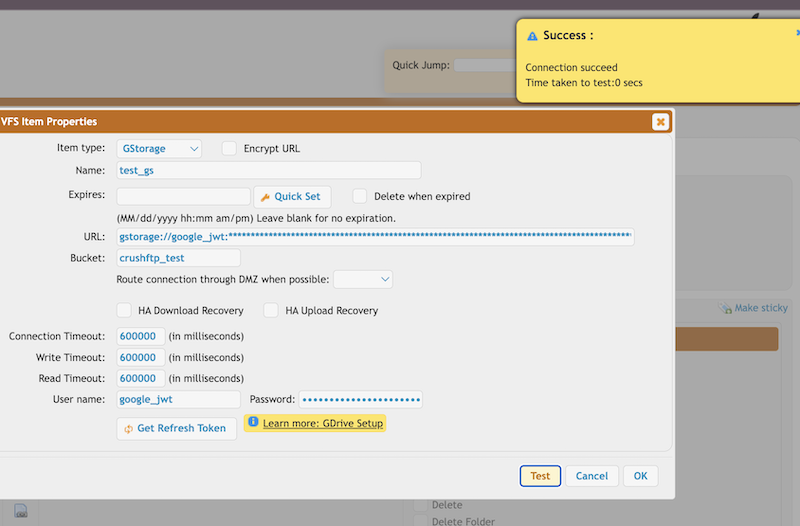
VFS configuration:
Username: google_jwt -> Special user name for Service Account Access.
Password: <<the JSON file content>> -> It authenticates based on the provided JSON file.
Provide the bucket and the path.
It is done! Test the connection and save it!
2. Access through S3 REST API#
Generate Access key and Secret. Got to Google Console Cloud Link In the left sidebar of the dashboard, click on the Google Cloud Storage and then Settings.
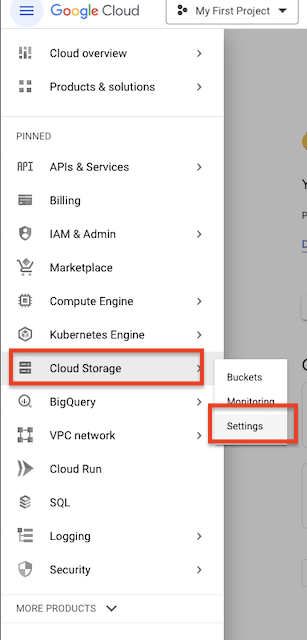
Select the Interoperability tab. If you haven't enabled it already, click on Interoperable Access. Now you should see an empty list and a Create New Key button. Click the button to create an Access/Secret key pair.
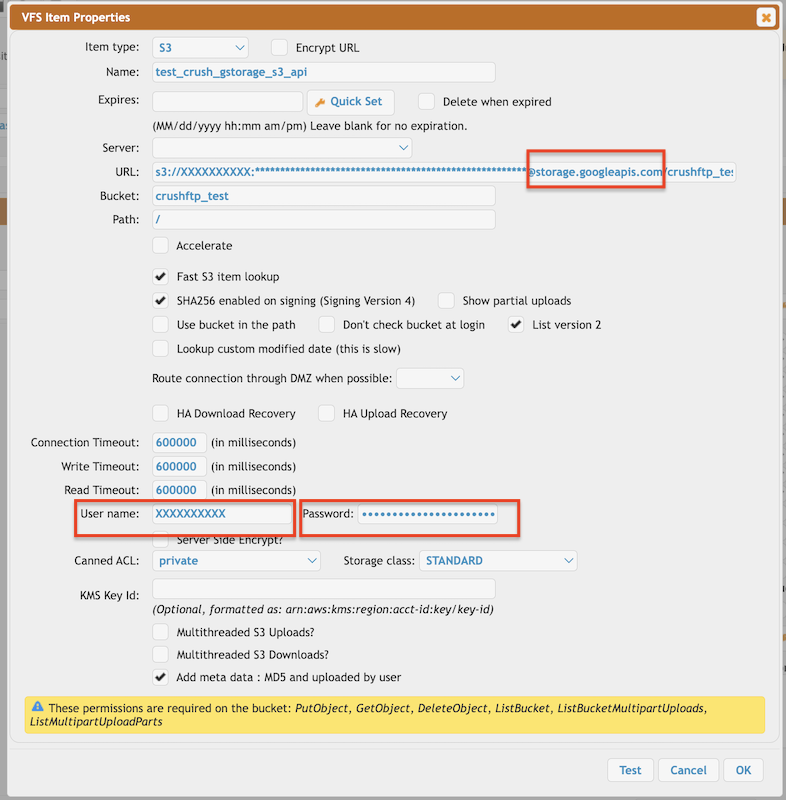
Google Cloud S3 VFS configuration:
1.
Domain: <<Cloud Storage -> Settings -> INTEROPERABILITY -> Domain of Storage URI default is storage.googleapis.com>>
Change the S3 default domain (s3.amazonaws.com) to the domain of Google Cloud Storage domain.
User name:<<Access Key>>
Password:<<Secret>>
Bucket:<<Google Cloud Storage Bucket Name>>
SHA256 enabled on signing (Signing Version 4):<<Enabled>>
⚠️ Signing version 4 must be enabled, as Google Cloud Storage does not support older signing versions.
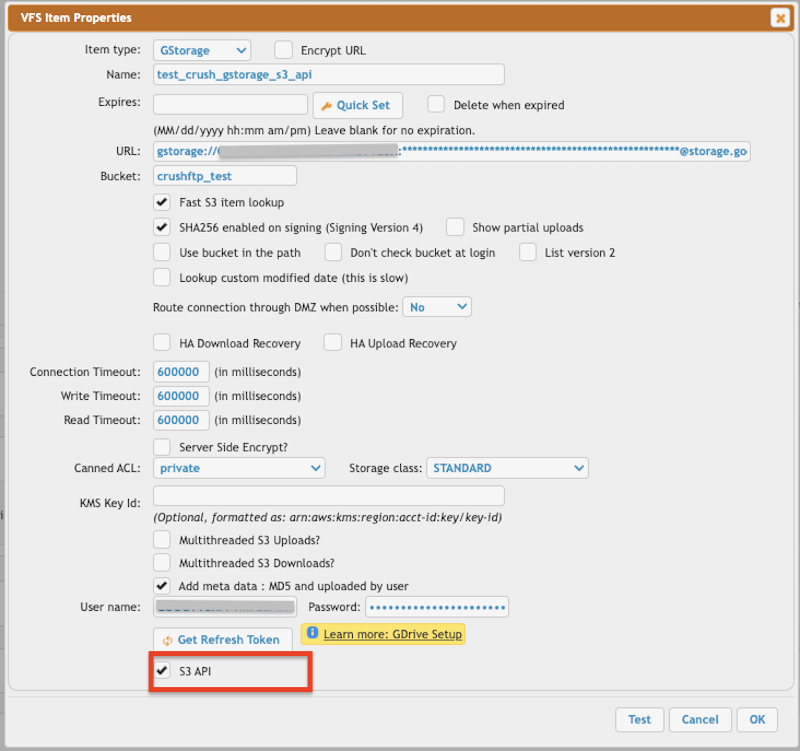
2. Select GStorage Item type.
Enable S3 API flag.
Domain:<<Cloud Storage -> Settings -> INTEROPERABILITY -> Domain of Storage URI default is storage.googleapis.com>>
Change the S3 default domain (s3.amazonaws.com) to the domain of Google Cloud Storage domain.
User name: <<Access Key>>
Password: <<Secret>>
Bucket: <<Google Cloud Storage Bucket Name>>
SHA256 enabled on signing (Signing Version 4):<<Enabled>>
⚠️ Signing version 4 must be enabled, as Google Cloud Storage does not support older signing versions.
More info about s3 VFS configuration: S3 integration