SSL#
SSL / TLS#
If you already have a JKS, PFX, or PKCS12 keystore file, you do not need to import this. This is a complete file and ready for CrushFTP to use. Just browse and choose this file, entering the password twice.
The top half of the page allows you to generate a new certificate by doing all 3 Steps in order. SSLCerts
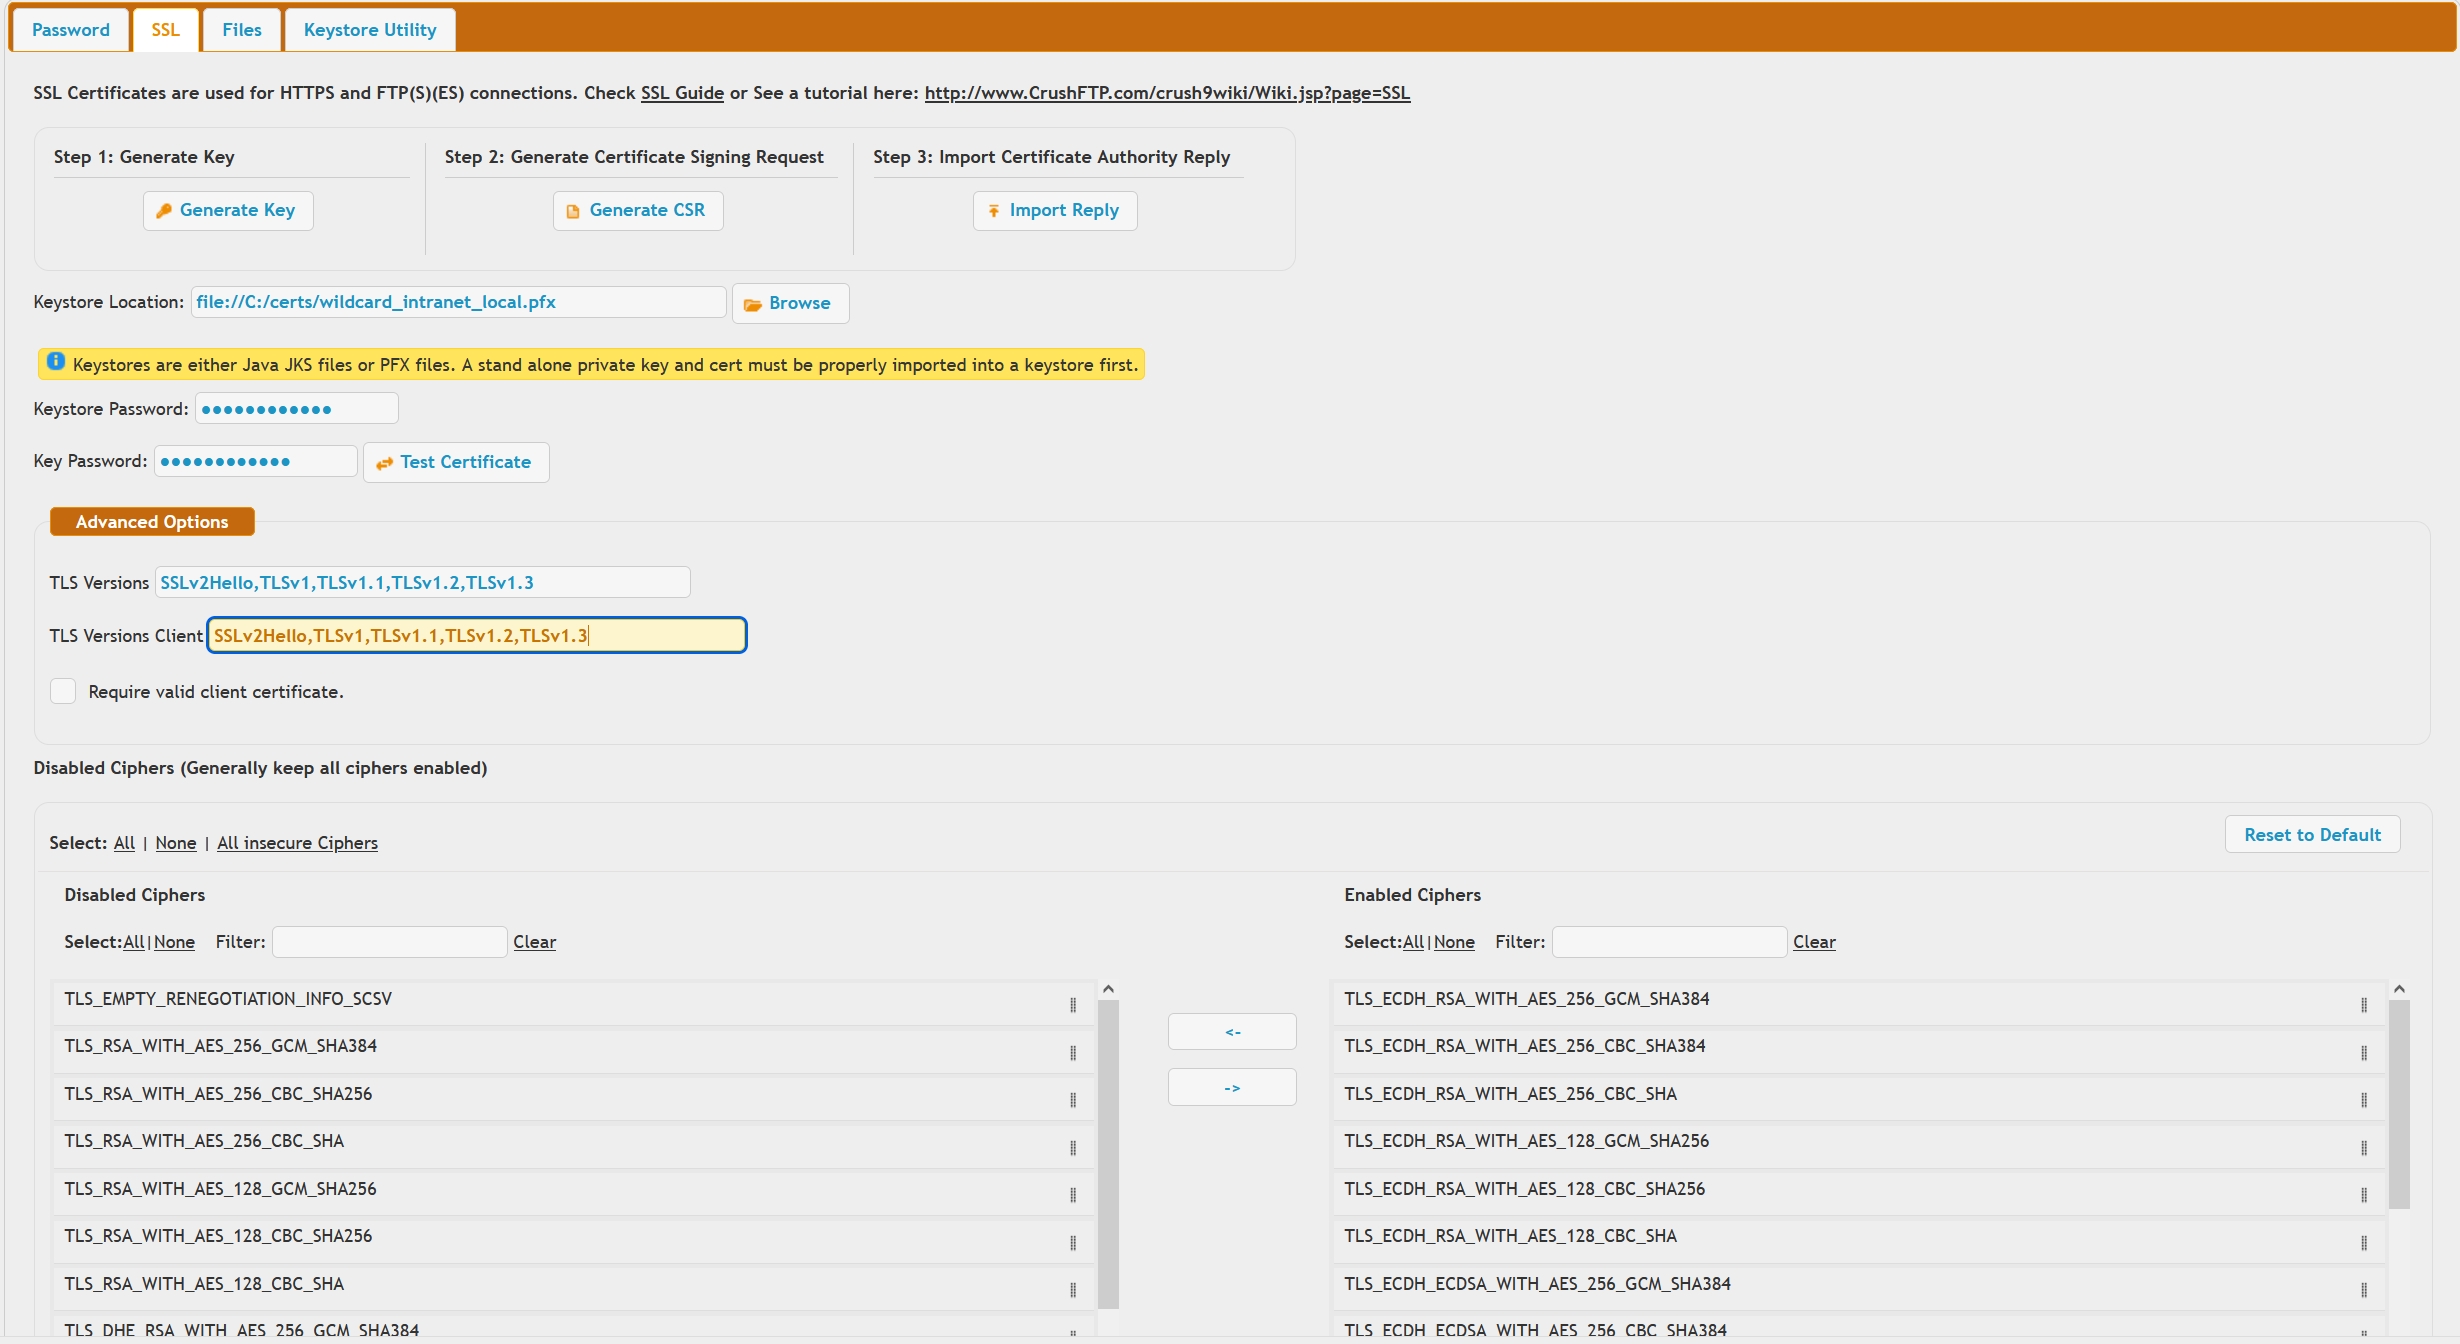
The Advanced section allows changing supported SSL cipher groups or enabling/disabling individual ciphers.
CrushFTP supports SSLv2Hello,TLSv1,TLSv1.1,TLSv1.2,TLSv1.3.
TLSv1.3 requires Java 17+. We recommend only using TLSv1.2 and TLS v1.3. (TLS session resumption for FTPS/FTPES is only supported by TLSv1.3 and Java 17+.)
TLS versions field defines the supported TLS versions the server ports will use: HTTPS, FTPS, FTPES.
TLS versions client field defines the supported TLS versions for all outbound client connections. This includes SMTP, HTTPS (outbound), FTP(S)(ES) (outbound), etc connections globally throughout the application.
Require valid client certificate , this is a rare feature when a remote server or your server is enforcing client client cert authentication SSL/TLS. This should be configured individually on the server port instead of globally.
The All insecure ciphers link will move all non 'A' rated ciphers into the Disabled ciphers list, we update the strength policy by CrushFTP updates as new ciphers come into existence or vulnerabilities are discovered in existing ones.